> For the complete documentation index, see [llms.txt](https://developer.harness.io/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://developer.harness.io/continuous-delivery/use-continuous-delivery/cd-building-blocks/cd-steps/containerized-steps/wiz-artifact-scan.md).
# Artifact scans with Wiz
Scan container image and repository artifacts with Wiz, using Orchestration or Ingestion mode, from a containerized step group
You can set up a Wiz step to run automated scans in a Harness pipeline. This step scans the container image you specify using the Wiz CLI. Harness Security Testing Orchestration (STO) then correlates, deduplicates, and ingests the scan results. Go to the [Vulnerabilities](https://developer.harness.io/docs/security-testing-orchestration/view-security-test-results/view-scan-results/) tab of the pipeline execution to view your scan results.
{% hint style="info" %}
**Wiz CLI upgrade notice**
The Wiz CLI is upgraded from version `0.x` to `1.x`. Harness STO supports this upgrade transparently, and no pipeline changes are required. CLI version `0.x` continues to work with existing credentials, while CLI version `1.x` requires new credentials. Credentials used with CLI `0.x` are not supported in CLI `1.x`.
{% endhint %}
***
## What you will learn from this topic
* How to [set up an Orchestration scan or an Ingestion scan](#set-up-workflows) for artifacts
* How to configure the [Wiz step settings](#wiz-step-settings-reference), including [scan mode](#scan), [target](#target), and [authentication](#authentication)
* How to [view Wiz policy failures](#view-wiz-policy-failures) and use [proxy settings](#proxy-settings)
* How to use a [sample pipeline](#sample-pipeline) for Orchestration mode or Ingestion mode
***
## Before you begin
To scan an artifact with Wiz, you need the following:
* A CI Build or Security Tests stage in your pipeline.
* A [Kubernetes](https://developer.harness.io/docs/continuous-integration/use-ci/set-up-build-infrastructure/k8s-build-infrastructure/set-up-a-kubernetes-cluster-build-infrastructure/) or [Docker](https://developer.harness.io/docs/continuous-integration/use-ci/set-up-build-infrastructure/define-a-docker-build-infrastructure/) build infrastructure, if you are running an Orchestration scan.
* [Harness text secrets](https://developer.harness.io/docs/platform/secrets/add-use-text-secrets/) for your `client-id` and `client-secret` to authenticate with the Wiz CLI, and for your image registry access ID and access token, if your registry requires authentication.
***
## Important notes for running Wiz scans in STO
The following notes apply when you run Wiz scans in STO:
* You can set up your STO scan images and pipelines to run scans as non-root and establish trust for your proxies using custom certificates. For more information, go to [Configure your pipeline to use STO images from private registry](https://developer.harness.io/docs/security-testing-orchestration/use-sto/set-up-sto-pipelines/configure-pipeline-to-use-sto-images-from-private-registry/).
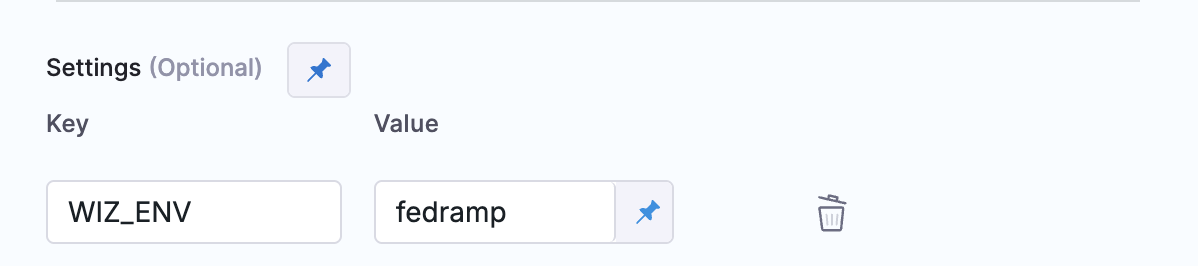
* If you use Wiz for Gov or GovCloud on Linux or macOS, configure the `WIZ_ENV` environment variable in your Wiz stage settings.
* For `app.wiz.us` (Wiz for Gov, FedRAMP), set `WIZ_ENV=fedramp`.
* For `gov.wiz.io` (GovCloud), set `WIZ_ENV=gov`.
***
## Set-up workflows
Choose the workflow that matches whether you want Harness to run the Wiz CLI scan (Orchestration) or ingest scan results produced outside the Wiz step (Ingestion).
Orchestration scans for artifacts
The setup process for Kubernetes and Docker build infrastructures has a few additional steps and requirements.
PrerequisitesA Kubernetes or Docker build infrastructure.Harness text secrets if your image registry requires an access ID and access token.Harness text secrets for your client-id and client-secret to authenticate with the Wiz CLI.Add a Docker-in-Docker background stepOrchestrated image scans on Kubernetes or Docker build infrastructures require a Docker-in-Docker (DinD) Background step.Add the Wiz scannerPerform the following steps to add the Wiz scanner:Add a CI Build or Security stage to your pipeline.Add a Wiz step to the stage.Set up the Wiz scanner using the required and optional settings below\.Required settingsScan mode = Orchestration.Target type = Container image.Target and Variant Detection = Auto.Under Container image:Type.Domain: Required only if you are using a registry with a non-standard domain, such as a private registry.Name: For example, jsmith/myimage.Tag: For example, latest.Authentication: Required only if the registry requires authentication:Registry access ID as a Harness secret.Registry access token as a Harness secret.Authentication:Wiz access ID as a Harness secret. This is your client-id to authenticate with the Wiz CLI.Wiz access token as a Harness secret. This is your client-secret to authenticate with the Wiz CLI.Optional settingsFail on Severity: Stop the pipeline if the scan detects any issues at a specified severity or higher.Log Level: Useful for debugging.PrerequisitesHarness text secrets if your image registry requires an access ID and access token.Harness text secrets for your client-id and client-secret to authenticate with the Wiz CLI.Add the Wiz scannerPerform the following steps to add the Wiz scanner:Add a Build or Security stage to your pipeline.Add a Wiz step to the stage.Set up the Wiz scanner using the required and optional settings below\.Required settingsScan mode = Orchestration.Target type = Container image.Target and Variant Detection = Auto.Under Container image:Type.Domain: Required only if you are using a registry with a non-standard domain, such as a private registry.Name: For example, jsmith/myimage.Tag: For example, latest.Authentication: Required only if the registry requires authentication:Registry access ID as a Harness secret.Registry access token as a Harness secret.Authentication:Wiz access ID as a Harness secret. This is your client-id to authenticate with the Wiz CLI.Wiz access token as a Harness secret. This is your client-secret to authenticate with the Wiz CLI.Optional settingsFail on Severity: Stop the pipeline if the scan detects any issues at a specified severity or higher.Log Level: Useful for debugging.
Ingestion scans for artifacts
{% hint style="info" %}
**JSON is the recommended ingestion format**
Harness STO can ingest both JSON and SARIF data from Wiz. Harness recommends publishing to JSON because this format includes more detailed information.
{% endhint %}
**Add a shared path for your scan results**
Perform the following steps to add a shared path:
1. Add a Build or Security stage to your pipeline.
2. In the stage **Overview**, add a shared path such as `/shared/scan_results`.
**Copy scan results to the shared path**
There are two primary workflows to copy scan results to the shared path:
* Add a Run step that runs a Wiz scan from the command line and then copies the results to the shared path.
* Copy results from a Wiz scan that ran outside the pipeline.
For more information and examples, go to [Ingestion scans](https://developer.harness.io/docs/security-testing-orchestration/key-concepts/ingest-scan-results-into-an-sto-pipeline/).
**Set up the Wiz scanner**
Add a Wiz step to the stage and set it up as follows.
**Required settings**
1. [Scan mode](#scan) = **Ingestion**.
2. [Target type](#target) = **Container Image**.
3. [Target name](#target): Usually the image name, such as `jsmith/myimage`.
4. [Target variant](#target): Usually the image tag, such as `latest`. You can also use a [runtime input](https://developer.harness.io/docs/platform/variables-and-expressions/runtime-input-usage/) and specify the tag at runtime.
5. [Ingestion file](#ingestion-file): For example, `/shared/scan_results/wiz-scan.json`.
**Optional settings**
* [Fail on Severity](#fail-on-severity): Stop the pipeline if the scan detects any issues at a specified severity or higher.
* [Log Level](#log-level): Useful for debugging.
***
## Wiz step settings reference
The recommended workflow is to add a Wiz step to a Security Tests or CI Build stage, and then configure the settings below.
### Scan
**Scan Mode** sets whether the step runs a new Wiz CLI scan (**Orchestration**) or ingests results produced outside the step (**Ingestion**). Go to [Wiz step settings reference](https://developer.harness.io/docs/security-testing-orchestration/sto-techref-category/wiz/artifact-scans-with-wiz/#scan) for the full description of each mode.
### Target
**Type**, **Target and Variant Detection**, **Variant**, and **Workspace** identify the artifact being scanned. Go to [Wiz step settings reference](https://developer.harness.io/docs/security-testing-orchestration/sto-techref-category/wiz/artifact-scans-with-wiz/#target) for the full description of each field.
**Name**
The identifier for the [target](https://developer.harness.io/docs/security-testing-orchestration/key-concepts/targets-and-baselines/), such as `jsmith/myalphaservice`. Descriptive target names make it easier to navigate your scan data in the STO UI.
It is good practice to [specify a baseline](https://developer.harness.io/docs/security-testing-orchestration/key-concepts/targets-and-baselines/#every-target-needs-a-baseline) for every target.
### Container image
**Type**, **Domain**, **Name**, **Tag/Digest**, **Access ID**, and **Access Token** identify and authenticate to the registry that hosts the scanned image. Go to [Wiz step settings reference](https://developer.harness.io/docs/security-testing-orchestration/sto-techref-category/wiz/artifact-scans-with-wiz/#container-image) for the full description of each field.
### Ingestion File
The path to your scan results when running an [Ingestion scan](https://developer.harness.io/docs/security-testing-orchestration/key-concepts/ingest-scan-results-into-an-sto-pipeline/), for example `/shared/scan_results/wiz.latest.json`.
* The data file must be in a [supported format](https://developer.harness.io/docs/security-testing-orchestration/whats-supported/scanners/#supported-ingestion-formats) for the scanner.
* The data file must be accessible to the scan step. It is good practice to save your results files to a shared path in your stage. In the visual editor, go to the stage where you are running the scan, and then go to **Overview** -> **Shared Paths**. You can also add the path to the YAML stage definition, for example:
```yaml
- stage:
spec:
sharedPaths:
- /shared/scan_results
```
### Authentication
**Access ID**
This is your `client-id` to authenticate with the Wiz CLI.
**Access Token**
This is your `client-secret` to authenticate with the Wiz CLI.
Create a Harness text secret with your encrypted token, and reference the secret using the format `<+secrets.getValue("my-access-token")>`. For more information, go to [Add and reference text secrets](https://developer.harness.io/docs/platform/secrets/add-use-text-secrets/).
### Log Level
Set the logging verbosity for the Wiz CLI. Go to [Wiz step settings reference](https://developer.harness.io/docs/security-testing-orchestration/sto-techref-category/wiz/artifact-scans-with-wiz/#log-level) for the full description.
### Additional CLI flags
Pass additional flags directly to the Wiz CLI.
{% hint style="warning" %}
**Advanced feature**
Passing CLI flags is an advanced feature. Some flags might not work in the context of STO. Test your flags and arguments thoroughly before you use them in your production environment.
{% endhint %}
### Fail on Severity
Stop the pipeline if the scan detects any issues at a specified severity or higher.
### Settings
You can add more settings to the scan step as needed.
### Additional Configuration
The fields under **Additional Configuration** vary based on the type of infrastructure. Depending on the infrastructure type you select, some fields might not appear in your settings.
* **Override Security Test Image**: [Container Registry](https://developer.harness.io/docs/security-testing-orchestration/use-sto/set-up-sto-pipelines/configure-pipeline-to-use-sto-images-from-private-registry/#step-level-override) and [Image Tag](https://developer.harness.io/docs/security-testing-orchestration/use-sto/set-up-sto-pipelines/configure-pipeline-to-use-sto-images-from-private-registry/#step-level-override).
* [Privileged](https://developer.harness.io/docs/continuous-integration/use-ci/manage-dependencies/background-step-settings/#privileged)
* [Image Pull Policy](https://developer.harness.io/docs/continuous-integration/use-ci/manage-dependencies/background-step-settings/#image-pull-policy)
* [Run as User](https://developer.harness.io/docs/continuous-integration/use-ci/manage-dependencies/background-step-settings/#run-as-user)
* [Set Container Resources](https://developer.harness.io/docs/continuous-integration/use-ci/manage-dependencies/background-step-settings/#set-container-resources)
* [Timeout](https://developer.harness.io/docs/continuous-integration/use-ci/run-step-settings/#timeout)
### Advanced settings
In **Advanced**, you can use the following options:
* [Conditional Execution](https://developer.harness.io/docs/platform/pipelines/step-skip-condition-settings)
* [Failure Strategy](https://developer.harness.io/docs/platform/pipelines/failure-handling/define-a-failure-strategy-on-stages-and-steps)
* [Looping Strategy](https://developer.harness.io/docs/platform/pipelines/looping-strategies/looping-strategies-matrix-repeat-and-parallelism)
* [Policy Enforcement](https://developer.harness.io/docs/platform/governance/policy-as-code/harness-governance-overview)
***
## View Wiz policy failures
Wiz policy failure results appear in the scan results as an `Info` level issue, categorized as an `External Policy` issue type. Go to [Wiz step settings reference](https://developer.harness.io/docs/security-testing-orchestration/sto-techref-category/wiz/artifact-scans-with-wiz/#view-wiz-policy-failures) for the full procedure to configure external policy failures and map them to a severity level.
***
## Proxy settings
This step supports private network connectivity if you use Harness Cloud infrastructure. Go to [Wiz step settings reference](https://developer.harness.io/docs/security-testing-orchestration/sto-techref-category/wiz/artifact-scans-with-wiz/#proxy-settings) for the `HTTPS_PROXY`, `HTTP_PROXY`, and `NO_PROXY` variable definitions and configuration steps.
***
## Sample Pipeline
The following examples show a sample pipeline for each scan mode.
Sample YAML: Orchestration mode
```yaml
pipeline:
name: cd-wiz-orchestration
identifier: cdwizorchestration
projectIdentifier: your_project_identifier
orgIdentifier: your_org_identifier
tags: {}
stages:
- stage:
name: s1
identifier: s1
description: ""
type: Deployment
spec:
deploymentType: Kubernetes
service:
serviceRef: your_service_identifier
environment:
environmentRef: your_environment_identifier
deployToAll: false
infrastructureDefinitions:
- identifier: your_infrastructure_identifier
execution:
steps:
- stepGroup:
name: sg
identifier: sg
steps:
- step:
type: Wiz
name: Wiz_1
identifier: Wiz_1
spec:
mode: orchestration
config: default
target:
type: container
detection: manual
name: test
variant: test
advanced:
log:
level: info
privileged: true
image:
type: docker_v2
tag: 14-alpine
name: library/node
domain: docker.io
auth:
access_token: your_access_token
access_id: your_access_id
stepGroupInfra:
type: KubernetesDirect
spec:
connectorRef: your_k8s_connector
rollbackSteps: []
tags: {}
failureStrategies:
- onFailure:
errors:
- AllErrors
action:
type: StageRollback
```
Sample YAML: Ingestion mode
```yaml
pipeline:
name: wiz-ingestion1
identifier: wizingestion1
projectIdentifier: your_project_identifier
orgIdentifier: default
tags: {}
stages:
- stage:
name: s1
identifier: s1
description: ""
type: Deployment
spec:
deploymentType: Kubernetes
service:
serviceRef: your_service_identifier
environment:
environmentRef: your_environment_identifier
deployToAll: false
infrastructureDefinitions:
- identifier: your_infrastructure_identifier
execution:
steps:
- stepGroup:
name: sg1
identifier: sg1
steps:
- step:
type: Run
name: Run_1
identifier: Run_1
spec:
connectorRef: a
image: alpine
shell: Sh
command: |-
cat <> example.json
{
"meta":{
"key":[
"issueName",
"fileName"
],
"subproduct":"MyCustomScanner"
},
"issues":[
{
"subproduct":"MyCustomScanTool",
"issueName":"Cross Site Scripting",
"issueDescription":"Lorem ipsum...",
"fileName":"homepage-jobs.php",
"remediationSteps":"Fix me fast.",
"risk":"high",
"severity":8,
"status":"open",
"referenceIdentifiers":[
{
"type":"cwe",
"id":"79"
}
]
}
]
}
EOF
ls
cat example.json
- step:
type: Wiz
name: Wiz_1
identifier: Wiz_1
spec:
mode: ingestion
config: default
target:
type: repository
detection: manual
name: external-scanner-test
variant: main
advanced:
log:
level: info
privileged: true
ingestion:
file: example.json
stepGroupInfra:
type: KubernetesDirect
spec:
connectorRef: your_k8s_connector
rollbackSteps: []
tags: {}
failureStrategies:
- onFailure:
errors:
- AllErrors
action:
type: StageRollback
```
***
## Next steps
* Go to [Containerize step groups](/continuous-delivery/use-continuous-delivery/cd-building-blocks/cd-steps/containerized-steps/containerized-step-groups.md) to run this step on your Kubernetes cluster.
* Go to [Background step](/continuous-delivery/use-continuous-delivery/cd-building-blocks/cd-steps/containerized-steps/background-step.md#docker-in-docker-dind) to configure the Docker-in-Docker step an Orchestration scan requires.
* Go to [What's supported in STO](https://developer.harness.io/docs/security-testing-orchestration/whats-supported/sto-deployments/), [Security Testing Orchestration FAQs](https://developer.harness.io/docs/security-testing-orchestration/faqs/), and [Optimize STO pipelines](https://developer.harness.io/docs/security-testing-orchestration/use-sto/set-up-sto-pipelines/optimize-sto-pipelines/) for more on setting up scanner integrations in STO.
{% @harness-feedback/feedback %}