> For the complete documentation index, see [llms.txt](https://developer.harness.io/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://developer.harness.io/web-application-and-api-protection-waap-discovery-discovery-api-security-testing/protection/bot-protection/bot-actors-and-accounts.md).
# Bot Actors and Accounts
Use the Bot Actors and Accounts page to identify automated entities that abuse, enumerate, or otherwise misuse your APIs
Updates (October 2026 to December 2026)
* *October 2026*: Updated the topic to reflect the latest user interface.
The Bot Actors and Accounts page helps you identify automated entities interacting with your APIs. These entities represent bots engaged in API abuse, enumeration, or other activities. Traceable analyzes traffic patterns and groups suspicious activity into bot actors and accounts.
## What you will learn from this topic
By the end of this topic, you will be able to:
* Understand how Traceable detects and classifies bot actors and accounts.
* Use insights on the Bot Actors and Accounts page to analyze activity.
* Investigate a bot actor in detail.
* Interpret activity patterns and behavior.
* Assess the impact of automated traffic across your APIs.
***
## Understand bot actors and accounts
The Bot Actors and Accounts page provides a centralized view of automated activity across your APIs, helping you understand where bot activity originates, how it behaves, and which accounts and APIs it targets. By analyzing activity across actors, accounts, events, and sessions, you can identify recurring patterns, detect coordinated or high-volume attacks, and investigate potential account takeover or credential abuse. These insights help you assess the impact of bot activity, prioritize high-risk actors and accounts, and create or refine Bot Protection policies with targeted controls.
The following table outlines why and when to use this view and how to leverage it for bot investigation and protection.
| Why use it? | When to use it? | How can you leverage it? |
| ----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- | --------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- | ------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------ |
| Understand the sources, behavior, and targets of automated activity. Identify coordinated attacks, recognize patterns across actors and accounts, and assess the impact on your APIs and users. | Investigate suspicious bot activity, identify targeted accounts, validate potential account takeover or credential abuse, and determine whether attacks are persistent, distributed, or time-bound. | Filter and group actors and accounts to identify common targets and attack patterns. Use these insights to prioritize risks and create or refine Bot Protection policies with targeted controls. |
***
## Navigate the bot actor and accounts workflow
On the **Bot Actors and Accounts** page, you see a consolidated list of detected actors along with key attributes, such as threat type, targeted APIs, and severity. The following is a list of metrics that are visible on the **Bot Actors and Accounts** dashboard:
Bot Actor and Accounts
The following tabs discuss the bot actors and accounts in detail:
{% tabs %}
{% tab title="Actors" %}
The bot actors tab highlights the key components of the bot actors dashboard:
* **Actor**: It represents the source of activity using attributes, such as IP address and user agent.
* **Actor Type**: It represents how the actor is identified or classified based on detection logic.
* **Threat Type**: It represents the type of behavior detected, such as scraping or credential abuse.
* **Targets**: It represents the APIs or endpoints the actor interacts with.
* **Labels**: It represents additional contextual tags that help enrich and categorize the actor's activity.
* **Severity**: It represents the risk level associated with the actor to help prioritize investigation.
* **Events Count**: It represents the total number of events generated by the actor, reflecting activity volume.
* **Accounts Count**: It represents the number of accounts impacted by the actor, reflecting downstream impact.
* **First Detected**: It represents when the activity was first detected.
* **Last Detected**: It represents when the activity was last detected.
#### Drill down into a specific actor
After you identify an actor, you open it to analyze behavior at a granular level. This view helps you understand how the actor operates and the extent of its impact. The actor detail view highlights attributes such as targeted APIs, associated accounts, severity, and behavioral indicators. It also provides contextual insights into how the activity is detected and why it is considered suspicious. The following metrics provide insights about a specific actor:
* **Total Events**: Total number of bot events generated by the actor.
* **Total Devices**: Number of devices linked to the actor.
* **Total IPs**: Total number of IP addresses detected.
* **Active Duration**: Time span over which the actor remains active, the difference between the first and last detected time.
The detailed view provides a deeper, granular understanding of bot actor behavior, activity patterns, and relationships across accounts and APIs. The following section highlights the metrics to analyze bot actor behavior, activity patterns, and account relationships:
The **Activity** tab highlights attributes, such as targeted APIs, associated accounts, severity, and behavioral indicators. It also provides contextual insights into how the activity is detected and why it is considered suspicious. You select an actor from the list to access detailed information, including identity attributes, activity patterns, and time-based behavior.
The following key activity metrics provide insights into actor behavior:
* **Endpoint**: APIs targeted by the actor help you identify focus areas and sensitive flows.
* **Events**: Total number of events generated indicates activity volume and intensity.
* **Accounts**: The number of impacted accounts shows how broadly the activity affects entities.
* **Last Seen**: The most recent activity timestamp helps you determine whether the activity is ongoing.
* **AI Summary**: Generated summary of observed behavior provides a quick interpretation of patterns and potential intent.
Bot Actor Detailed View Activity Tab
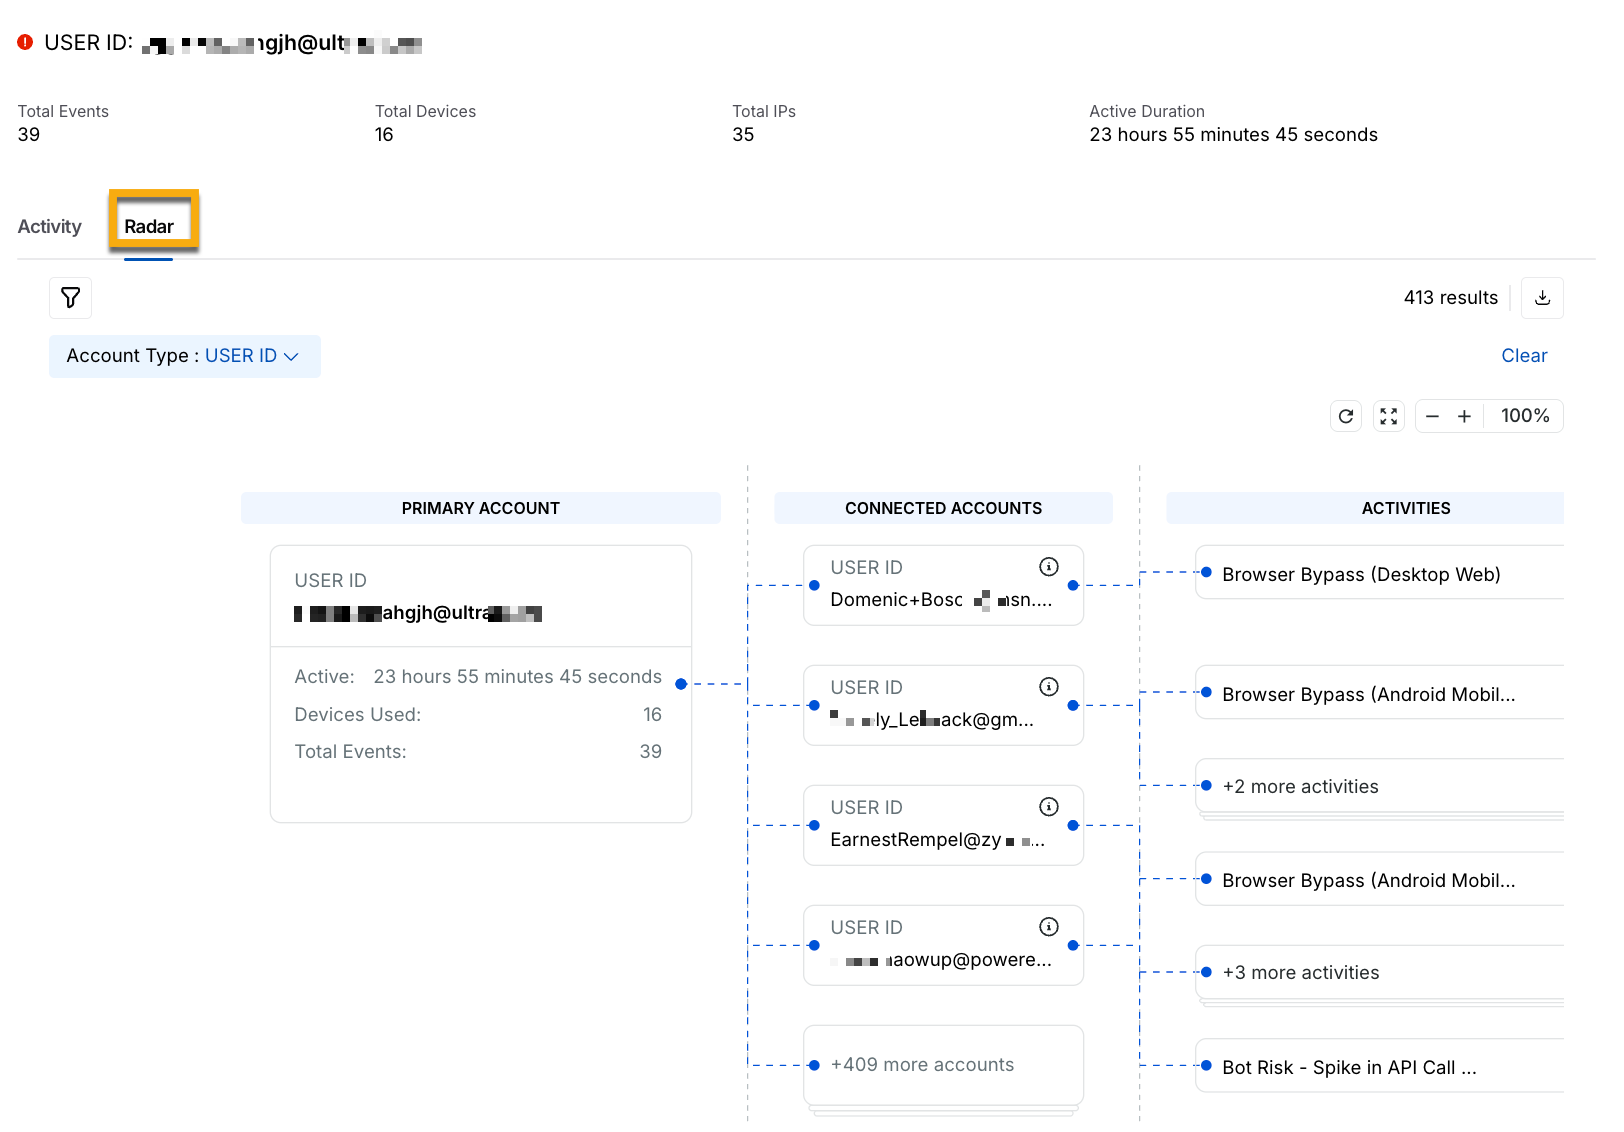
The **Radar** tab helps you identify the primary source account from where the bot attack started. It shows you the sequential network of connected accounts involved in the attack. You can filter (:filter:) accounts by account type, threat type, and target using the filter icon. The following screenshot shows the different detected accounts flow:
Bot Actor Detailed View Radar Tab
The following table displays the components of the flowchart at each level:
| Primary Account | Connected Accounts | Activity |
| -------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- | ------------------------------------------------------- | -------------------------------------------------------------------------------- |
|
User ID: Unique identifier of the primary account.
Active Duration: Total time the account is active. It is the difference between the last and first detected times.
Devices Used: Devices associated with the account.
Total Events: Total number of recorded events.
| **User ID**: Identifiers of linked or related accounts. | **Activities**: Activities associated with the threat that violate bot policies. |
This helps you analyze the connected accounts and track any suspicious activity across them.
{% endtab %}
{% tab title="Accounts" %}
The bot accounts tab highlights the key components of the bot accounts dashboard:
This section identifies and tracks accounts using attributes, such as user ID. When activity increases in frequency or severity, Traceable flags the account as *risky*. The following section gives you an overview of the metrics:
* **Total** **risky accounts**: Number of impacted accounts.
* **Trend visualization**: Activity changes over time.
* **Top attacked endpoints**: The most attacked endpoints. These insights help you spot spikes, detect patterns, and identify ongoing attacks early.
When you drill into an account, you can review detailed evidence at the event level. You can examine request and response data and compare the activity against expected user behavior. This helps you understand how the attack works and confirm whether the activity is malicious.
On the same page, the following metrics provide a summary of account-level activity and help you assess the nature, scale, and impact:
* **Account**: Indicates the source of activity using attributes, such as IP address, user agent, or device fingerprint. This helps you understand who is interacting with the account.
* **Account Type**: Indicates how the account is classified according to the detection logic. This helps you determine whether the source is known, suspicious, or unknown.
* **Threat Type**: Indicates the type of automated behavior detected, such as scraping or credential abuse. This helps you understand the nature of the attack.
* **Targets**: Indicates the APIs or endpoints that it accesses. This helps you identify which application flows are being targeted.
* **Labels**: Indicates contextual tags that enrich and categorize the activity. This helps add clarity and additional classification.
* **Severity**: Indicates the risk level associated with the activity. This helps you prioritize investigation and response.
* **Events Count**: Indicates the total number of events generated. This reflects the volume and intensity of activity. When you click an event count, you are redirected to the [Bot Events](https://developer.harness.io/web-application-and-api-protection-waap/protection/bot-protection/bot-events) page.
* **Actor Count**: Indicates the number of actors involved. This helps you understand the scale of impact. When you click an actor count, you are redirected to the bot actors tab.
* **First Detected**: Indicates when the activity was first detected.
* **Last Detected**: Indicates when the activity was last detected.
After you identify an account, you can analyze behavior at a granular level. This view helps you understand how the account operates and the extent of its impact. The account detail view highlights attributes, such as targeted APIs, associated accounts, severity, and behavioral indicators. It also provides contextual insights into how the activity is detected and why it is considered suspicious. The following metrics provide insights about a specific account:
* **Total Events**: Total number of bot events generated by the account.
* **Total Devices**: Number of devices linked to the account.
* **Total IPs**: Total number of IP addresses detected.
* **Active Duration**: Time span over which the actor remains active, the difference between the first and last detected time.
You also gain access to event-level evidence, such as request and response data, timestamps, and account attributes, enabling detailed analysis of how the automation operates. You can get a more granular level understanding of the bot accounts from the **Activity** and the **Radar** tabs below:
* **Activity:** This tab provides detailed account metrics, helping you dive deep into analysis. The following metrics provide deeper visibility into account-level activity:
* **Activity**: It represents the detected behavior patterns associated with the account, helping you quickly understand the type and nature of automation affecting it.
* **Endpoint**: It represents the APIs or application endpoints accessed, allowing you to identify which flows are being targeted.
* **Events**: It represents the total number of events generated for the account, indicating the volume and intensity of activity.
* **Actors**: It represents the number of distinct entities interacting with the account, helping you determine whether the activity originates from a single source or multiple coordinated sources.
* **Last Seen**: It represents the most recent activity timestamp, showing whether the activity is ongoing.
* **AI Summary**: It generates a concise interpretation of observed behavior, providing a quick overview of patterns and potential intent.
* **Radar:** This tab helps you identify the primary source account from where the bot attack started. It shows you the sequential network of connected accounts involved in the attack. You can filter accounts by *account type*, *threat type*, and *target*. The flowchart contains the following table, which displays the components of the flowchart at each level:
| Primary Account | Connected Accounts | Activity Overview |
| ------------------------------------------------------ | ------------------------------------------------------ | -------------------------------------------------------------------------------- |
| **User ID**: Unique identifier of the primary account. | | |
| **Active Duration**: Total time the account is active. | **User ID**: Identifiers of linked or related accounts | |
| **Devices Used**: Devices associated with the account. | | **Activities**: Activities associated with the threat that violate bot policies. |
| **Total Events**: Total number of recorded events. | | |
This view helps you move from identifying impacted accounts to understanding the depth, pattern, and intent of the activity, enabling more effective investigation and response. This helps you analyze the connected accounts and track any suspicious activity across them.
{% endtab %}
{% endtabs %}
***
## Investigate bot actors and accounts
The following section discusses investigating a bot actor and account in detail:
### Investigate a bot actor
Investigate a bot actor by analyzing its request patterns, targeted API endpoints, authentication attempts, error responses, and retry behavior. Examine whether it targets one or multiple accounts and look for repetitive or coordinated activity. Compare these patterns with expected application behavior to classify the activity as benign, suspicious, or malicious. If intent remains unclear, continue monitoring before taking restrictive action.
#### Sample scenarios
The following section explains sample scenarios in which bot protection policies, actors, and accounts work together to prevent and manage bot attacks:
Example 1: Detecting and mitigating account enumeration
You observe repeated requests to your user verification endpoints and navigate to the Bot Actors page. One actor is making frequent attempts using different email addresses to check which accounts exist. The activity is systematic, with no legitimate variation in behavior, and impacts multiple accounts. Based on these signals, you classify the actor as performing account enumeration. You apply mitigations, such as implementing rate limits, introducing response obfuscation, and triggering alerts for suspicious patterns.
Example 2: Prevent automated API abuse
Traffic analysis reveals excessive requests to your pricing and checkout endpoints. On the Bot Actors page, a specific actor stands out with high-frequency requests exceeding normal usage patterns. The requests follow a uniform cadence, often targeting sensitive operations, such as creating orders or fetching pricing data, indicating automated misuse rather than legitimate activity. You classify the actor as engaging in API abuse and enforce controls, such as request throttling, authentication checks, and anomaly alerts. Post-mitigation monitoring confirms that abuse has been mitigated and that the API remains secure.
Example 3: Identify credential-stuffing attacks
You notice a spike in login attempts across multiple user accounts. A single actor is submitting numerous login requests targeting authentication endpoints, often in bursts from different IP addresses. The requests show repeated use of common credentials with no variation, indicating automated credential stuffing. You classify the actor accordingly and implement protective measures such as account lockouts, rate limiting, and enforcement of multi-factor authentication.
### **Investigate a bot account**
Bot activity does not appear as a single signal. It surfaces through repeated attempts, anomalous request behavior, and coordinated activity across accounts. The investigation focuses on identifying patterns, narrowing the scope, and validating activities with evidence. You can follow these steps to investigate bot accounts more efficiently and identify attacks more effectively.
#### Step 1: Identify accounts that require attention
On the Bot Accounts page, accounts are listed with severity, event volume, and actor count. Scan the dataset to identify accounts that stand out due to activity spikes, recurring threat types, or irregular time patterns. Prioritize high-severity accounts and those with large event volumes. Use the actor count to determine whether the activity is isolated or distributed; a higher count indicates potential coordination.
#### Step 2: Analyze account activity in context
Open the account detail view to examine activity over time. Use the timeline and event distribution to understand how activity evolves, including continuous traffic, burst patterns, and API coverage. Repeated authentication attempts, access to sensitive flows, and deviations from baseline usage indicate abnormal behavior and help distinguish suspicious activity from expected usage.
#### Step 3: Correlate activity with bot actors
You can switch to bot actors to understand how the activity is attributed. Determine whether a single actor targets multiple accounts or multiple actors target a single account, as these patterns indicate different attack strategies. Compare shared attributes, such as IP patterns, request structures, and behavioral consistency, to establish relationships between actors and accounts.
#### Step 4: Validate findings with event data
Drill down into event-level data to review activity in detail. Analyze requests and responses, including payloads, response codes, and failure patterns, to determine intent. Repeated authentication failures and structured request sequences indicate automated activity. Distinguish malicious behavior from legitimate automation, such as integrations or testing traffic, before taking action.
#### Step 5: Assess impact and scope
Assess how far the activity extends across the environment by evaluating event frequency, duration, and the number of affected accounts or APIs. Determine whether multiple actors are involved to understand if the activity is coordinated. Broader distribution and longer duration indicate higher impact and help prioritize response.
#### Step 6: Identify patterns across accounts
Expand the analysis to identify related activity across accounts. Use filtering and grouping to detect similar behavior, shared threat types, and common actors. Repeated patterns across accounts indicate campaign-level activity rather than isolated incidents and help connect findings into a broader attack pattern.
***
## Filters and grouping
You can filter and group different bot actors and accounts for better analysis. This helps you understand the impact, prioritize response, and uncover how the bot actor or the account affects you. This view helps you quickly identify high-risk actors and prioritize investigation. You can refine your analysis using the following options:
* Select the environment you require from the **Environment** drop-down.
* Choose a specific period to analyze threats using the **Time** **filter**.
* Organize accounts by *threat type* or *target* using the **Group By** option.
* Filter (:filter:) and sort based on investigation needs.
* Export data (:file-export:) for further analysis.
You can then drill down into any actor or account for detailed investigation. For deeper analysis, you access event-level evidence associated with the actor. This includes request and response data, actor attributes, timestamps, and behavioral signals, allowing you to understand how the automation operates and what it targets.
***
## Demo
The following demo walks you through the steps to navigate and investigate deep into your bot actors and accounts:
{% embed url="" %}
{% @harness-feedback/feedback %}